Enterprise SSO and VPN: Entra ID and Keycloak
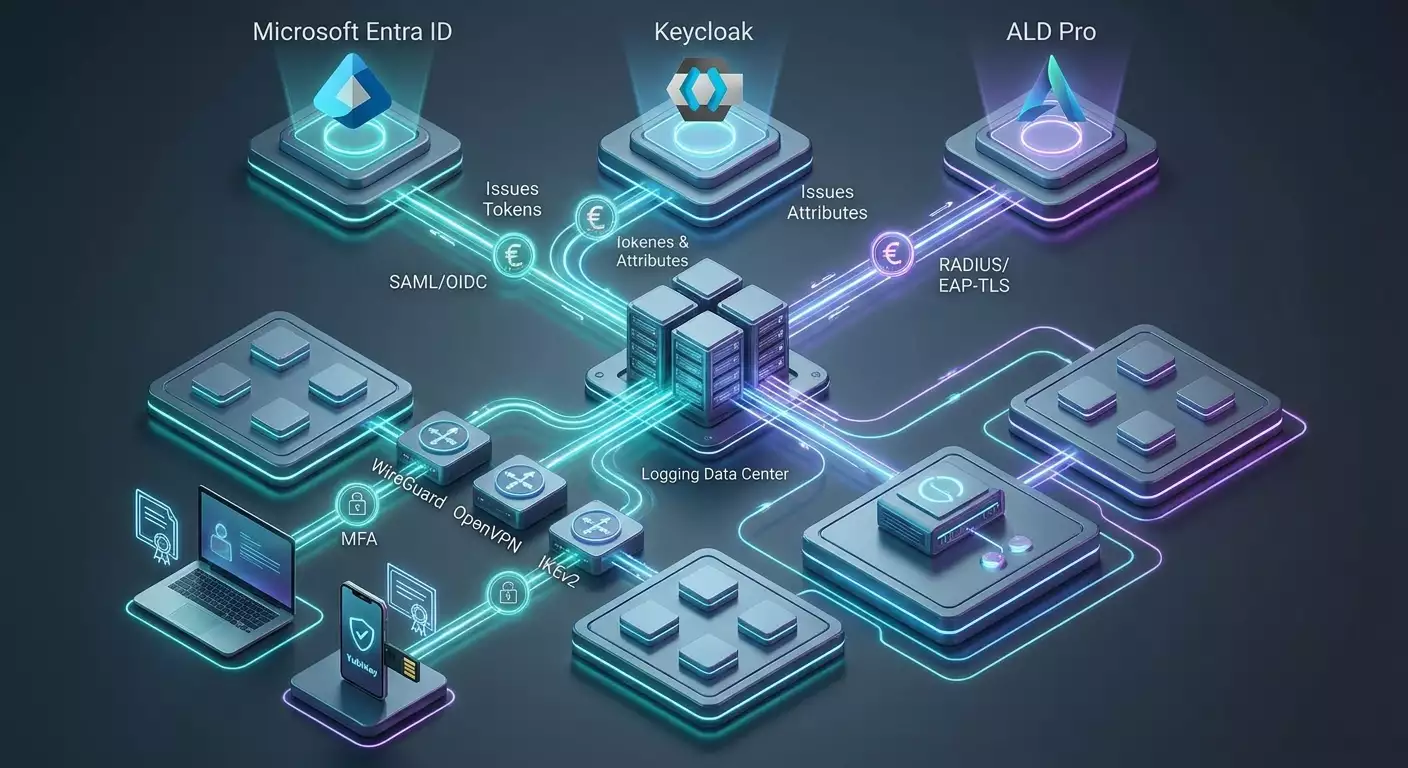
Entra ID and Keycloak provide identity, not a replacement VPN gateway. Select a supported SAML/OIDC or RADIUS integration and verify revocation actually ends access; plain WireGuard does not implement SSO by itself.
Content of the article
Entra ID and Keycloak provide identity, not a replacement VPN gateway. Select a supported SAML/OIDC or RADIUS integration and verify revocation actually ends access; plain WireGuard does not implement SSO by itself.
Practical checks
Start with an inventory of users, applications, branches and data flows. Assign access ownership and responsibility for revoking privileges. A VPN supplies a network channel; it does not replace device management, identity, resilience or an assessment of applicable requirements. Do not promise legal compliance based only on a protocol or server country.
Verify compatibility of the exact gateway, client and identity-provider versions before rollout. Allow only required routes and roles; successful authentication must not open the entire network. Use supported MFA, certificate verification and protected secrets storage. Confirm integrations in product documentation rather than assuming support from a technology name.
Pilot with a limited group and test resources. Check normal login, denied access, device changes, user revocation, node failure and recovery. Agree acceptance criteria first: recovery time, permitted loss, application availability and log completeness. Keep the original configuration and a step-by-step rollback. Define the minimum log fields, retention and viewer permissions; avoid unnecessary collection of user traffic content.
Official documentation
Publisher: vpn.how